AI Safety Rules Hit Reality
AI Safety Rules Hit Reality
The AI race has stopped being a clean story about smarter chatbots and productivity gains. It is now a test of whether governments, companies, and the public can manage systems that are powerful, opaque, and increasingly embedded in daily life. AI safety rules are no longer a theoretical debate for policy panels. They are becoming a business constraint, a trust signal, and, for some companies, a competitive weapon. The uncomfortable truth is simple: the same models that can draft code, summarize documents, and accelerate research can also amplify scams, misinformation, bias, and security failures at industrial scale. That tension is forcing a new phase for artificial intelligence: less hype, more accountability, and far more scrutiny over what happens after a model leaves the lab.
- AI safety is becoming operational: Companies now need testing, monitoring, incident response, and governance around
AI models. - Regulation is shifting the market: Compliance may favor well-funded incumbents while raising the bar for smaller startups.
- Transparency is the new trust layer: Users, regulators, and enterprise buyers want clearer evidence of how systems behave.
- The biggest risks are not only futuristic: Fraud, bias, data leakage, and security abuse are already here.
- Safety can become a product advantage: Firms that prove reliability may win the next wave of adoption.
Why AI Safety Rules Matter Now
The first wave of generative AI felt like a software launch. The second wave looks more like infrastructure. That shift matters because infrastructure has failure modes. A buggy photo filter is annoying. A faulty AI assistant that mishandles medical advice, legal reasoning, financial workflows, or security decisions is something else entirely.
Regulators are responding because the incentives around AI are unusually combustible. Companies are rewarded for speed, scale, and capability. Users are rewarded for convenience. Bad actors are rewarded for automation. Without guardrails, the market naturally pushes toward deployment first and cleanup later.
Key insight: The central AI policy question is no longer whether models are impressive. It is whether they are dependable enough to deserve the roles companies are giving them.
This is where AI safety rules become more than paperwork. They force developers to ask basic but expensive questions: What data trained this system? What can it reveal? What decisions can it influence? Who is liable when it fails? How quickly can abuse be detected? And crucially, should the system be deployed at all?
AI Safety Rules Are Becoming a Business Test
For years, tech companies treated safety as a mix of content moderation, public relations, and internal research. That model is no longer enough. Enterprise customers want procurement-grade assurances before connecting large language models to private data, customer support, software repositories, or internal decision systems.
That creates a new kind of due diligence. Buyers are not just asking whether a model is faster or cheaper. They are asking whether it supports audit logs, role-based access, data isolation, prompt monitoring, abuse detection, and human review. These features sound less glamorous than benchmark scores, but they are becoming decisive in real deployments.
The Compliance Gap Will Reshape Competition
The companies best positioned for stricter rules are often the ones with legal teams, security teams, policy teams, and enough revenue to absorb compliance costs. That could benefit major cloud providers and large AI labs. It could also make life harder for startups that rely on rapid iteration and open distribution.
There is a real trade-off here. Strong oversight may reduce reckless deployments, but overly complex regimes can entrench incumbents. If only the largest firms can afford to run extensive model evaluations, produce documentation, and maintain regulatory interfaces, the AI market may become safer but less open.
Pro Tip: For startups building with AI, safety should not be bolted on before a funding round or enterprise sales call. It should be part of the product architecture from day one, including data handling, fallback behavior, and escalation paths.
The Technical Reality Behind AI Safety Rules
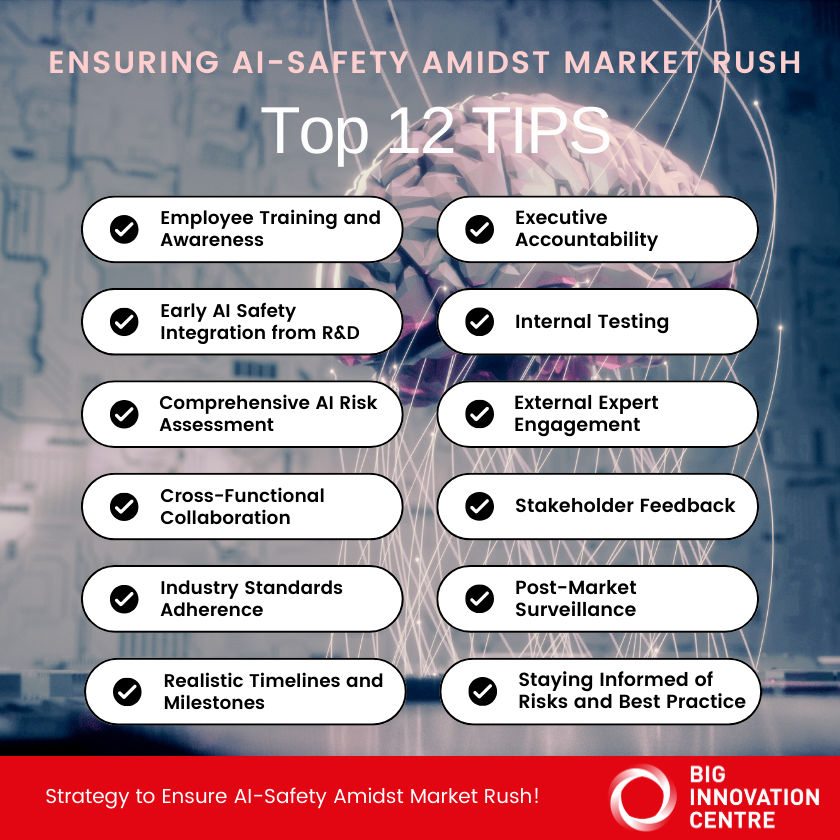
AI safety sounds abstract until it becomes a checklist. The practical work is technical, repetitive, and often unglamorous. It includes stress-testing model outputs, simulating adversarial prompts, monitoring behavior after release, and documenting known limitations.
Modern AI systems are not traditional software. Developers cannot simply inspect every line of logic because much of the behavior emerges from training data, model weights, reinforcement techniques, and user interaction. That makes testing harder. It also means safety cannot depend on a single pre-launch review.
Evaluation Is Not One Test
A serious evaluation program looks at multiple risk layers. There are accuracy tests, bias tests, security tests, privacy tests, and misuse tests. A model that performs well on academic benchmarks may still fail when exposed to messy real-world prompts, multilingual content, or coordinated abuse.
Some of the most important questions include whether a model can produce dangerous instructions, leak sensitive data, generate persuasive disinformation, or comply with manipulative user requests. These are not edge cases. They are predictable outcomes when powerful tools become widely available.
Monitoring Matters After Launch
Pre-release testing is necessary, but it is not enough. Models encounter new prompts, new attack methods, and new social contexts after deployment. That means companies need live monitoring and incident response. In practice, that may involve red teaming, automated abuse detection, user reporting tools, and clear rollback procedures.
This is where many organizations underestimate the challenge. Deploying an AI feature is easy. Maintaining a safe AI feature at scale is harder. The work resembles cybersecurity: the threat landscape changes, attackers adapt, and yesterday’s mitigation can become tomorrow’s weak point.
AI Safety Rules and the Data Problem
Data remains the quiet center of the AI safety debate. Models are trained on huge datasets, often assembled from public web content, licensed material, user interactions, and synthetic data. That creates three major risks: privacy, copyright, and contamination.
Privacy risk appears when systems memorize or expose sensitive information. Copyright risk appears when training data includes protected material without clear permission. Contamination risk appears when a model is trained or evaluated on flawed, biased, duplicated, or manipulated data.
For businesses, the immediate concern is data leakage. If a company connects an AI tool to internal documents, customer records, or source code, it must know where that information goes. Does it train future models? Is it stored? Who can access it? Can it be deleted? These are no longer niche security questions. They are board-level governance issues.
Why Users Should Care About AI Safety Rules
Most users will never read a model card, inspect a system prompt, or compare evaluation benchmarks. But they will feel the consequences of weak safety practices. They may receive fake customer support messages, AI-generated scams, biased automated decisions, or plausible but incorrect answers presented with total confidence.
The risk is not that AI will always be wrong. The risk is that it will often be convincing. That makes human judgment more important, not less. Users need visible cues when content is AI-generated, clear routes to appeal automated decisions, and better disclosure when AI systems are involved in sensitive contexts.
The skeptical view: If people cannot tell when AI is being used, cannot challenge its output, and cannot trace responsibility for harm, then safety claims are mostly branding.
Good rules should make AI more legible. That does not mean revealing every trade secret. It means giving users and regulators enough information to understand the purpose, limits, and accountability structure of a system.
The Global Race to Define AI Safety Rules
AI governance is becoming a geopolitical issue. Different regions are taking different approaches, from risk-based regulation to voluntary commitments and sector-specific rules. The result is a fragmented compliance environment where global companies may have to satisfy multiple standards at once.
This fragmentation is frustrating, but it reflects a deeper reality: countries disagree about the proper balance between innovation, civil liberties, national security, and market power. AI is not just another software category. It touches defense, education, labor, media, healthcare, and democratic trust.
Companies that operate internationally will need governance systems flexible enough to handle different legal expectations. That means stronger internal controls, clearer documentation, and a more mature approach to product risk. The firms that treat regulation as a temporary annoyance will struggle. The firms that treat it as market infrastructure may gain credibility.
What Strong AI Safety Rules Should Include
Effective governance should be specific enough to matter and flexible enough to survive technical change. Overly vague promises invite abuse. Overly rigid mandates become obsolete. The strongest approach focuses on risk, evidence, and accountability.
- Clear risk tiers: Not every
AI toolneeds the same oversight, but high-impact uses should face tougher requirements. - Independent evaluation: Powerful systems should be tested by qualified third parties, not only internal teams.
- Incident reporting: Companies should disclose serious failures, abuse patterns, and mitigation steps.
- Data governance: Firms need clear rules for collection, consent, retention, and deletion.
- Human oversight: Sensitive decisions should include meaningful human review, not symbolic approval.
The best rules will not eliminate AI risk. No serious framework can promise that. But they can reduce predictable harms, improve response times, and create consequences for negligent deployment.
The Future of AI Safety Rules
The next stage of AI will likely be defined by agents: systems that do not just answer questions but take actions across software, browsers, databases, and workplace tools. That raises the stakes. A chatbot that gives a bad answer is a problem. An AI agent that sends the wrong email, changes a file, books a transaction, or executes code creates a different category of risk.
As models gain more autonomy, safety rules will need to move closer to permissions architecture. What can the system access? What actions require confirmation? What happens if the model is manipulated by a malicious prompt hidden inside a document or webpage? These are not science fiction scenarios. They are engineering challenges already visible in early agentic systems.
The winners in this phase will not simply be the companies with the largest models. They will be the companies that make AI useful without making it reckless. That requires restraint, product discipline, and a willingness to measure success by more than engagement and speed.
AI Safety Rules Will Separate Hype From Trust
The AI industry is entering its accountability era. The excitement is real, and so is the risk. Strong AI safety rules will not stop innovation. Done well, they will make innovation durable by giving users, enterprises, and governments a reason to trust the systems being deployed around them.
The hard part is execution. Safety cannot be a press release, a vague ethics page, or a one-time benchmark. It has to be engineered into products, audited over time, and backed by consequences when companies cut corners. That is the difference between AI as a dazzling demo and AI as dependable infrastructure.
For readers, businesses, and policymakers, the signal to watch is not which model tops the latest leaderboard. It is which companies can prove their systems behave responsibly when incentives, attackers, and real-world complexity put them under pressure.
The information provided in this article is for general informational purposes only. While we strive for accuracy, we make no guarantees about the completeness or reliability of the content. Always verify important information through official or multiple sources before making decisions.